An RCSA is only useful if its risk assessments can withstand challenge and its controls work in practice. For Malaysian financial institutions, the difficult questions are often about ownership, evidence, inconsistent ratings, technology dependencies and whether remediation has actually reduced risk. This advanced program develops the judgement and practical skills needed to build credible RCSAs, assess control design and operating effectiveness, test key controls and turn findings into accountable action. Bank Negara Malaysia expectations are linked to the relevant exercises throughout, using Malaysian banking processes and examples applicable to Islamic banks, insurers and takaful operators. Delegates work through a continuing Malaysian banking scenario, supported by shorter cases on fraud, service disruption, outsourcing and Islamic financing operations. They leave with completed examples and templates to adapt within their own institutions.
 Two- day classroom program
Advanced Risk and Control Self-Assessment and Control Effectivenessfor Financial Institutions
This is an advanced level course and delegates should have working knowledge of operational risk and RCSA, or relevant experience in controls, compliance or assurance. Core concepts receive a brief calibration rather than an introductory treatment.
About the program?
- Challenge risk statements, assessment boundaries and inherent risk assumptions using process, incident and change information.
- Build an RCSA with clear risk and control ownership, defensible ratings and traceable evidence.
- Distinguish control design from operating effectiveness and assess dependencies, overrides and compensating controls.
- Design risk-based tests, justify sampling and evaluate exceptions without overstating assurance.
- Reassess residual risk and create remediation plans with measurable closure criteria.
- Connect RCSA findings with BNM expectations, risk appetite, loss events, KRIs and management decisions.
One Case Study from Risk Identification to a Completed RCSA
Throughout Modules 1–4, delegates will work through a continuing financial-institution case study, progressively building an RCSA as they learn. Starting with process mapping and risk identification, they will assess inherent risks, evaluate key controls and determine residual risk before defending their conclusions through structured peer challenge. This connected approach shows how each stage informs the next and gives delegates practical experience they can apply within their own institutions.
Booking options
Fee per participant
RM5,900/US$1,500 Enquire about this course →
Please note that the Ringgit price is applicable to Malaysia-domiciled participants only. Discounts are available for group bookings. Please contact us for more details.
*Price is subject to 8% Service Tax
Who should attend?
This program is designed for professionals responsible for assessing operational risk, maintaining effective controls and overseeing remediation in banks, insurers and takaful operators. It is particularly relevant to operational and enterprise risk teams, business and process owners, operations and shared services managers, compliance officers, internal auditors, and control assurance and GRC practitioners. Banking case studies form the core, with discussion of their application across other financial institutions.
Day One: Risk Assessment and RCSA Quality 27 January 2027
Module 1: Identifying and Assessing the Risks that Matter 5 topics
Objective: Moving beyond generic risk lists to identify how processes can fail, why they may fail and the potential impact on a financial institution.
- Apply process mapping, incidents, near misses, complaints, audit findings and business changes to identify material operational risk exposures.
- Develop meaningful risk statements by distinguishing causes, risk events and consequences, including related conduct and compliance impacts.
- Assess likelihood and impact across financial loss, customer harm, service disruption and regulatory consequences using informed judgement.
- Identify key people, process, system, data, technology and third-party dependencies that may increase operational risk exposure.
- Translate relevant BNM expectations into practical risk and control considerations across banking, insurance and takaful operations.
Case study and practical exercise: Examine a financial institution process to identify material operational risks, dependencies and control concerns. Develop clear risk statements and begin building the risk assessment that will be progressively used throughout Day One.
Module 2: Building a Credible and Meaningful RCSA 5 topics
Objective: Creating an RCSA that the business can own, Risk can effectively challenge and reviewers can understand and defend.
- Define appropriate RCSA scope, boundaries and assessment granularity while avoiding duplicated risks and gaps between processes.
- Establish clear risk and control ownership, review responsibilities and accountability across the first line, second line and independent assurance.
- Assess inherent risk consistently and challenge assumptions and inconsistent ratings across comparable risks and processes.
- Link risks to key controls, incidents, KRIs, issues, regulatory obligations and other relevant information to support evidence-based assessment.
- Maintain the RCSA as a dynamic risk management tool by identifying material incidents, product, process, system or outsourcing changes that should trigger reassessment.
Case study and practical exercise: Building on Module 1, develop the RCSA, assess inherent risks, identify key controls and challenge inconsistent assumptions and ratings using relevant BNM expectations.
Module 3: Assessing Control Design and Operating Effectiveness 5 topics
Objective: Moving beyond confirming that a control exists to determine whether it appropriately addresses the risk and operates effectively in practice.
- Establish clear control objectives, ownership, frequency, evidence and escalation requirements so that controls can be meaningfully assessed.
- Evaluate whether preventive, detective, manual, automated and compensating controls are appropriately designed to address the identified risk.
- Assess operating effectiveness using evidence and distinguish reliable control execution from policies, procedures, training or management assertions.
- Identify weaknesses arising from overrides and dependencies on people, access, systems, configuration and data quality.
- Determine whether control effectiveness supports the residual risk rating without mechanical rating reductions or double-counting related controls.
Case study and practical exercise: Assess key controls within the continuing RCSA scenario, examine available evidence and determine whether the control-effectiveness and residual-risk conclusions can be supported and defended.
Module 2: Building a Credible and Meaningful RCSA 5 topics
Objective: Creating an RCSA that the business can own, Risk can effectively challenge and reviewers can understand and defend.
- Define appropriate RCSA scope, boundaries and assessment granularity while avoiding duplicated risks and gaps between processes.
- Establish clear risk and control ownership, review responsibilities and accountability across the first line, second line and independent assurance.
- Assess inherent risk consistently and challenge assumptions and inconsistent ratings across comparable risks and processes.
- Link risks to key controls, incidents, KRIs, issues, regulatory obligations and other relevant information to support evidence-based assessment.
- Maintain the RCSA as a dynamic risk management tool by identifying material incidents, product, process, system or outsourcing changes that should trigger reassessment.
Case study and practical exercise: Building on Module 1, develop the RCSA, assess inherent risks, identify key controls and challenge inconsistent assumptions and ratings using relevant BNM expectations.
Module 4: Conducting and Challenging an End-to-End RCSA 5 topics
Objective: Bringing together risk identification, assessment and control evaluation to complete and defend an RCSA under structured challenge.
- Establish clear control objectives, ownership, frequency, evidence and escalation requirements so that controls can be meaningfully assessed.
- Evaluate whether preventive, detective, manual, automated and compensating controls are appropriately designed to address the identified risk.
- Assess operating effectiveness using evidence and distinguish reliable control execution from policies, procedures, training or management assertions.
- Identify weaknesses arising from overrides and dependencies on people, access, systems, configuration and data quality.
- Determine whether control effectiveness supports the residual risk rating without mechanical rating reductions or double-counting related controls.
Case study and practical exercise: Finalise the RCSA progressively developed through Modules 1–3 and defend key risk, control and residual-risk conclusions through structured peer challenge.
Day Two: Control Testing, Remediation and Risk Governance 28 January 2027
Module 5: Designing a Risk-Based Control Testing Programme 5 topics
Objective: Bringing together risk identification, assessment and control evaluation to complete and defend an RCSA under structured challenge.
- Prioritise key controls for testing using risk exposure, incidents, significant changes, previous findings and the strength of existing assurance.
- Define clear test objectives, populations, testing periods, evidence requirements and assessment criteria.
- Select appropriate testing techniques, including walkthrough, inspection, observation, reperformance and data analysis according to the control objective.
- Apply proportionate risk-based sampling and understand the limitations of judgemental sampling when drawing control-effectiveness conclusions.
- Assess automated and technology-dependent controls and determine when third-party assurance is sufficient or additional institution-level testing is required.
Case study and practical exercise: Design tests for selected key controls, develop practical test steps and evidence requirements, and justify the testing and sampling approach.
Module 6: Executing Control Tests and Interpreting Exceptions 5 topics
Objective: Turning control-testing evidence and exceptions into defensible conclusions about whether controls are operating effectively and whether residual risk remains appropriately assessed.
- Validate the completeness, relevance, reliability and timeliness of testing populations and supporting evidence before drawing conclusions.
- Execute and document testing so that the work performed, evidence examined and basis for conclusions can be independently understood and reviewed.
- Distinguish missing evidence, failed control execution and weaknesses in control design when analysing testing exceptions.
- Determine whether exceptions are isolated or potentially systemic and when further investigation or expanded testing is warranted.
- Assess the implications of testing results for control effectiveness, residual risk, remediation and escalation.
Case study and practical exercise: Examine control-testing evidence and exceptions, assess their significance and reach a defensible conclusion on control effectiveness and its implications for residual risk.
Module 7: Reporting Findings and Achieving Effective Remediation 5 topics
Objective: Turning identified control weaknesses into clear findings and remediation actions that address underlying causes and deliver sustainable risk reduction.
- Develop clear findings that explain the control weakness, underlying cause, risk impact and implications for the relevant control objective.
- Prioritise deficiencies according to actual risk exposure and urgency rather than exception count alone.
- Develop remediation actions that address root causes with accountable owners, realistic timelines and appropriate interim safeguards.
- Establish measurable closure criteria and distinguish completion of an action from evidence that the control is operating effectively and risk has been reduced.
- Strengthen governance over overdue actions, repeated extensions and risk acceptance, with appropriate escalation of significant or recurring weaknesses.
Case study and practical exercise: Challenge a proposed response to a recurring control failure and develop a practical remediation plan with clear ownership, interim safeguards and evidence required to demonstrate effective closure.
Module 8: Integrating RCSA and Control Testing into Risk Governance 5 topics
Objective: Translating RCSA and control-testing results into meaningful risk information that enables senior management and the Board to understand the organisation's operational risk profile and exercise effective oversight.
- Integrate material RCSA and control-testing results with relevant incidents, loss data, KRIs, control indicators and risk appetite information to develop a consolidated view of operational risk.
- Identify material changes in risk exposure, significant control weaknesses, recurring issues and overdue remediation requiring management or Board attention.
- Distinguish detailed operational information required by business and risk owners from information appropriate for senior management and Board oversight.
- Apply materiality and judgement to determine what should be reported, how much detail is appropriate and what matters require escalation or decision.
- Translate detailed RCSA information into concise management and Board reporting that highlights significant exposures, risk trends, control concerns, remediation status and decisions required.
Case study and practical exercise: Prepare a concise senior management or Board-level risk briefing using RCSA and control-testing information. Determine what should be escalated, the appropriate level of detail and the management or Board attention or decision required.
Expert Course Director
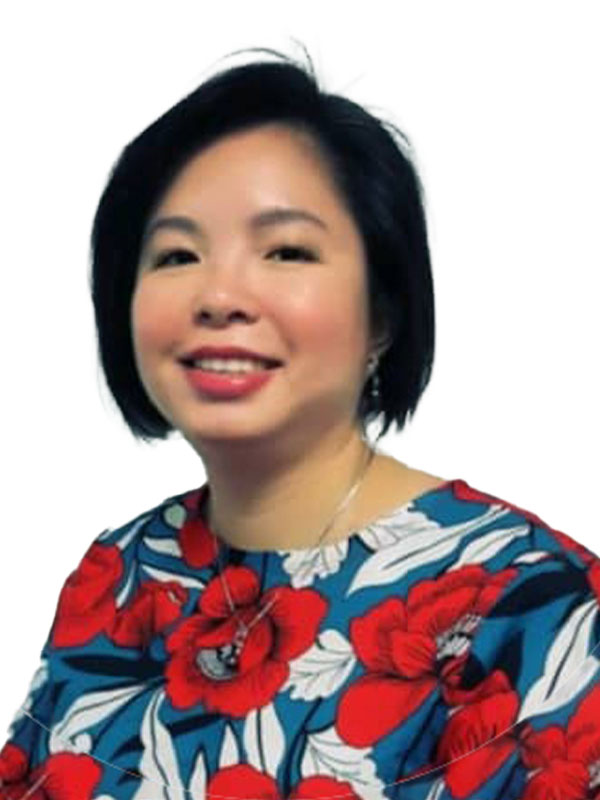
Lan Yann Erl
Lan Yann Erl is an experienced Governance, Risk & Compliance (GRC) practitioner with more than 26 years of leadership experience across Malaysia's financial services industry. She has held senior leadership positions with HSBC Bank Malaysia, Maybank, AmBank Group, United Overseas Bank (Malaysia) and Alliance Bank Malaysia, with extensive experience spanning regulatory compliance, compliance governance, operational risk management, operational resilience and control effectiveness. Throughout her career, Lan has led the design and enhancement of enterprise-wide governance, compliance and operational risk frameworks, translating regulatory expectations into practical policies, processes and controls. Her experience includes regulatory advisory, compliance risk management, regulatory engagement and breach reporting, control testing, issue and remediation oversight, business continuity management, outsourcing and third-party risk, product governance and Board reporting. Lan has held Head-level leadership roles in Group Regulatory Advisory, Compliance Governance, Group Operations Control and Operational Risk Management. She has worked extensively with Boards, Board Committees and senior management on governance and risk oversight and has significant experience engaging with Bank Negara Malaysia on regulatory, compliance and risk management matters. An HRD Corp Accredited Trainer, Chartered Banker, Fellow of the International Compliance Association (FICA) and Professional Member of the Institute of Operational Risk (PIOR), Lan combines extensive industry experience with a practical, practitioner-led training approach. Her programs focus on translating regulatory requirements and risk management principles into practical, business-relevant actions that participants can apply within their organizations.
Registration
Looking for training tailored to your team?
Whether you're planning a dedicated in-house programme or registering a group for one of our public seminars, we're here to help you find the right option.
Explore Training Options